Ruijie
RG-S6990-64OC2XS
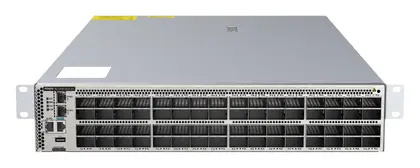
Ruijie RG-S6990-64OC2XS 64 Port 800G OSFP 2×10G SFP+ Veri Merkezi Switch
PoE yok

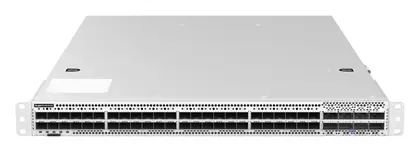
RG-S6000C-48GT4XS-ERuijie RG-S6000C-48GT4XS-E, 48 portlu gigabit bir yönetilebilir switch'tir.
Ruijie RG-S6000C-48GT4XS-E özellikleri ve kullanım alanları.
Full gigabit ports and flexible and scalable 10GE uplink data exchange capability, coping with data center problems such as massive device quantity, high cost, and traffic burst
The RG-S6000C-48GT4XS-E provides 48 x 1GE ports, 4 x 10GE ports, and 1 x expansion module slot. All ports support data forwarding at the line rate to better handle heavy east-west traffic. This makes the RG-S6000C-48GT4XS-E an ideal choice for non-blocking networking of data centers with heavy traffic demands.
The RG-S6000C-48GT4XS-E adopts the virtual switching unit (VSU) technology to virtualize multiple physical devices into one logical device, which reduces network nodes and enhances network reliability. The switch implements fast switchover within 50 ms to 200 ms upon a link failure, thereby ensuring uninterrupted transmission of critical service traffic. M-LAG enables the RG-S6000C-48GT4XS-E to connect to access servers and switches through dual-active uplinks.
The RG-S6000C-48GT4XS-E supports Virtual Ethernet Port Aggregator (VEPA) defined in IEEE802.1Qbg. It can divert data flows generated by virtual machines (VMs) on a server to a physical network device for hard switching. This implements traffic policing of VMs and enforces access control policies uniformly. Compared with soft switching, hard switching does not occupy server resources. All these make the next-generation data center network solution better adapt to the virtual computing environment.
The RG-S6000C-48GT4XS-E supports VM detection and automatic migration of security policies. Security policies can be deployed uniformly for VM traffic in a large-scale server virtualization environment. Moreover, it can be used with the data center network management platform and VM management control platform. In this context, security policies can be migrated accordingly when VMs migrate on the entire network. This prevents network security vulnerabilities in the server virtualization environment and improves network maintenance efficiency.
The RG-S6000C-48GT4XS-E supports modular power modules in 1+1 redundancy mode. All power modules and line cards can be hot swapped, and support overcurrent protection, overvoltage protection, and over temperature protection, ensuring device-level reliability.
The switch also supports a wide range of link-level reliability technologies including the Rapid Link Detection Protocol (RLDP), Rapid Ethernet Uplink Protection (REUP), and Virtual Router Redundant Protocol (VRRP), Spanning Tree Protocol (STP), Rapid Spanning Tree Protocol (RSTP), and Multiple Spanning Tree Protocol (MSTP). The switch also features Graceful Restart (GR) and Bidirectional Forwarding (BFD). On the network that carries multiple services and heavy traffic, these mechanisms enable fast network convergence and ensure smooth service rollout.
The hardware of the RG-S6000C-48GT4XS-E supports IPv4 and IPv6 protocol stacks and multilayer line-rate switching, and differentiates and processes IPv4 and IPv6 packets. The switch also supports multiple tunneling technologies such as manually configured tunnels and Intra-Site Automatic Tunnel Addressing Protocol (ISATAP) tunnels. It is flexibly applicable to IPv6 inter-network communication solutions based on IPv6 network planning and network status quo.
The switch supports abundant IPv4 routing protocols, including static routing, Routing Information Protocol (RIP), Open Shortest Path First (OSPF), Intermediate System to Intermediate System (IS-IS), and Border Gateway Protocol version 4 (BGP4).
The switch also supports various IPv6 routing protocols, including static routing, Routing Information Protocol next generation (RIPng), OSPFv3, IS-IS v6, and BGP4+. You can flexibly select an IPv6 routing protocol to upgrade the live network to an IPv6 network or establish a new IPv6 network.
The RG-S6000C-48GT4XS-E switch can effectively defend against virus and hacker attacks through multiple built-in mechanisms, such as DoS attack defense, IP scanning attack defense, ARP packet validity check, and multiple hardware-based ACLs.
The hardware-based IPv6 ACLs can easily control the access of IPv6 users at the network edge even if there are IPv6 users on an IPv4 network. The switch allows IPv4 and IPv6 users to coexist and can control access permissions of IPv6 users, for example, restricting access to sensitive resources on a network.
The switch provides CPU Protection Policy (CPP), an industry-leading hardware-based CPU protection mechanism. CPP enables the switch to classify data traffic sent to the CPU, process the traffic by queue priority, and apply rating limiting on traffic as required. CPP fully protects the CPU from being occupied by unauthorized traffic, malicious attacks, and resource consumption, which ensures the security of the CPU and switch.
The switch and its ports can be flexibly bound to a user's IP address and MAC address, which strictly restricts the access of users connected to the ports or the switch.
DHCP snooping enables the switch to receive DHCP messages only from trusted ports and prevent spoofing from unauthorized DHCP servers. With DHCP snooping, the switch dynamically monitors ARP packets, checks users' IP addresses, and discards unauthorized packets that do not match binding entries, thereby effectively preventing ARP spoofing and source IP address spoofing.
The switch supports Telnet access control based on source IP addresses, which prevents unauthorized users and hackers from attacking and controlling the switch, thus enhancing network management security.
Kurumsal ağlarda VLAN ile kamera, misafir ve ofis trafiğini ayırmak, uplink ve omurga bağlantılarını yönetmek için kullanılır.
Ruijie Cloud üzerinden uzaktan yapılandırma ve izleme yapılabilir.
Değerler üretici veri sayfasından derlenmiştir; proje öncesi güncel datasheet ile teyit edilmesi önerilir.
| Boyutlar (G x D x Y) | 440 mm x 300 mm x 44 mm (17.32 in. x 11.81 in. x 1.73 in.) |
|---|---|
| Kabin Yüksekliği | 1 RU |
| Cihaz Ağırlığı | 3.6 kg (7.94 lbs., empty chassis); 4.8 kg (10.58 lbs., a chassis with two power modules and one fan module) |
| Anahtarlama Kapasitesi | 256Gbps |
| Paket İletim Hızı | 192 Mpps |
| Servis Portu | 48 x 10/100/1000BASE-T ports; 4 x 10G/1G SFP+ ports |
| Yönetim Portu | 1 x RJ45 console port; 1 x RJ45 MGMT port |
| USB Portu | 1 x USB 2.0 port (Type A connector); 1 x mini-b USB 2.0 serial port |
| Modül Yuvası | 2 x power module slots; 1 x fan module slot |
| Güç Tüketimi | Maximum power consumption: 60 W; Typical power consumption: 50 W; Static power consumption: 34.2 W |
| Güç Girişi | RG-PA70I (AC input):; Rated input voltage: 100 V AC to 240 V AC, 50 Hz/60 Hz; Maximum input voltage: 90 V AC to 264 V AC, 47 Hz to 63 Hz; Rated input current: 2 A (100 V AC to 240 V AC); Power port type: C14; RG-PA70I (HVDC input):; Rated input voltage: 120 V DC to 340 V DC; Maximum input voltage: 110 V DC to 380 V DC; Rated input current: 2 A |
| Sıcaklık | Operating temperature: 0°C to 50°C (32°F to 122°F); Storage temperature: –40°C to +70°C (–40°F to +158°F); Note: At altitudes ranging from 3,000 m (9,842.52 ft.) to 5,000 m (16,404.20 ft.), the maximum temperature decreases by 1°C (1.8°F) for every 200 m (656.17 ft.) increase in elevation. |
| Nem | Operating humidity: 10% RH to 90% RH (non-condensing); Storage humidity: 5% RH to 95% RH (non-condensing) |
| Rakım | Operating altitude: ≤ 3,000 m (9,842.52 ft.); Storage altitude: ≤ 5,000 m (16,404.20 ft.) |
| Soğutma | Air cooling, front-to-rear airflow (port-side intake) |
| VLAN | 4K IEEE 802.1Q VLANs; Port-based VLAN; MAC-based VLAN; Protocol-based VLAN; Private VLAN; Voice VLAN; IP subnet-based VLAN; GVRP |
|---|---|
| QinQ | Basic QinQ; Selective QinQ; N:1 and 1:1 VLAN switching |
| Link Aggregation | LACP (IEEE 802.3ad) |
| SPAN | N:1 mirroring; 1:N mirroring; Traffic-based mirroring |
| Spanning Tree Protocol | STP, RSTP, and MSTP |
| DHCP | DHCP server; DHCP client; DHCP snooping; DHCP relay; IPv6 DHCP snooping; IPv6 DHCP client; IPv6 DHCP relay |
| Basic IPv6 protocols | IPv6 addressing, Neighbor Discovery (ND), ND Snooping, ICMPv6, Stateless Auto Configuration, Path MTU Discovery |
| IP Yönlendirme | Static routing; RIP, RIPng; OSPF, OSPFv3, IS-IS, IS-IS v6; BGP, BGP4+; Equal-cost multi-path routing (ECMP); Packet-based and traffic-based load balancing; Multi-VPN-Instance CE (MCE) |
| Multicast | IGMPv1/v2/v3 and IGMP proxy; IGMPv1/v2/v3 snooping; IGMP filtering, IGMP fast leave; PIM-DM, PIM-SM, PIM-SSM; MLD snooping, MLD; PIM for IPv6; MSDP |
| MPLS | MPLS forwarding, LDP, LSP |
| IPv6 tunneling | Manually configured tunnel, automatic tunnel, ISATAP, IPv4 over IPv6, GRE tunnel, and other tunneling technologies |
| ACL | The following flexible and diversified hardware ACLs are available:; Standard IP ACL (IP-based hardware ACL); Extended IP ACL (hardware ACL based on the IP address or TCP/UDP port ID); Extended MAC ACL (hardware ACL based on the source MAC address, destination MAC address, and optional Ethernet type); Time-based ACL; Expert-level ACL (hardware ACL based on flexible combinations of the VLAN ID, Ethernet type, MAC address, IP address, TCP/UDP port ID, protocol type, and time); ACL80; IPv6 ACL |
| QoS | Port traffic identification; Port traffic rate limiting; 802.1p/DSCP/ToS traffic classification; Eight priority queues per port; SP, WRR, DRR, SP+WFQ, SP+WRR, SP+DRR, and RED/WRED queue scheduling |
| Security features | 3-tuple binding (IP address, MAC address, and port); 3-tuple binding (IPv6 address, MAC address, and port); MAC address filtering; Port- and MAC-based 802.1x authentication; MAC Bypass Authentication (MAB); Portal authentication and Portal 2.0 authentication; ARP check; Dynamic ARP inspection (DAI); ARP rate limiting; ARP spoofing prevention; Broadcast storm suppression; Hierarchical management and password protection; RADIUS and TACAS+; AAA (IPv4/IPv6) for device login management; SSH and SSHv2 |
| Management features | SNMPv1/v2c/v3, CLI (Telnet/Console), RMON (1,2,4,9), SSH, Syslog, NTP/SNTP, SNMP over IPv6, IPv6 MIB support for SNMP, SSHv6, Telnet v6, FTP/TFTPv6, DNSv6, NTP for v6, Traceroute v6; sFLOW using the random sampling technology to conduct flow information sampling on the switch traffic |
| High reliability | VSU; GR for RIP, GR for OSPF, GR for BGP, and GR for other routing protocols; BFD; ERPS (G.8032); REUP; RLDP; 1+1 power redundancy; One modular fan module with front-to-rear airflow; 2+1 fan redundancy; Hot swapping of power modules |
| Energy Efficient Ethernet (EEE) | IEEE 802.3az-compliant EEE: When EEE is enabled, power consumption of ports is significantly reduced. |
| Çalışma Sıcaklığı | 0°C to 50°C (32°F to 122°F) |
|---|---|
| Çalışma Nemi | 10% RH to 90% RH (non-condensing) |
Veri sayfası ve kullanım kılavuzları.
RG-S6000C-48GT4XS-E hakkında kısa yanıtlar.
Formu doldurun, RG-S6000C-48GT4XS-E için fiyat ve teslim süresini iletelim.