Juniper
Teknik özellikler
Üretici veri sayfasından derlenmiştir; proje öncesi güncel datasheet ile teyit edilmesi önerilir.
Teknik Özellikler 7 satır
| Ortalama Isı Yayılımı | 1 x DC PSU (40V): 653.4 BTU/h 2 x DC PSU (40V): 737 BTU/h 1 x AC PSU (110V): 682 BTU/h 1 x AC PSU (230V): 662 BTU/h 2 x AC PSU (110V): 703 BTU/h 2 x AC PSU (230V): 682 BTU/h |
|---|---|
| Advanced Threat (CPS**) | 6 Gbps |
| Connections per second (64B) | 450,000 |
| SSL connections per second | 8,000 |
| Maks. Eşzamanlı Oturum (IPv4/IPv6) | 5 Million |
| Route table size (RIB/FIB) (IPv4) | 2 Million/1.2 Million |
| IPSec VPN Tünel Sayısı | 4,000 |
Environment and Regulatory Compliance 6 satır
| Hava Akışı / Soğutma | Front to back |
|---|---|
| Çalışma Sıcaklığı | 32°F to 104°F (0°C to 40°C at 6000 ft altitude) |
| Çalışma Nemi | 5% to 90% non-condensing |
| MTBF | Over 100,000 hours (12 years) |
| FCC classification | Class A |
| RoHS compliance | RoHS 6 |
Performans ve Ölçek 7 satır
| Firewall throughput 2 (IMIX) | 28 Gbps |
|---|---|
| Firewall throughput 2 (1518B) | 39 Gbps |
| IPSec VPN throughput 2 (IMIX) | 18 Gbps |
| IPSec VPN throughput 2 (1400B) | 36 Gbps |
| Application security performance (TPS # /CPS**) | 36 Gbps/23 Gbps |
| Next-generation firewall (TPS # /CPS**) | 35 Gbps/12 Gbps |
| Secure Web Access Firewall (CPS**) | 11 Gbps |
Genel bakış
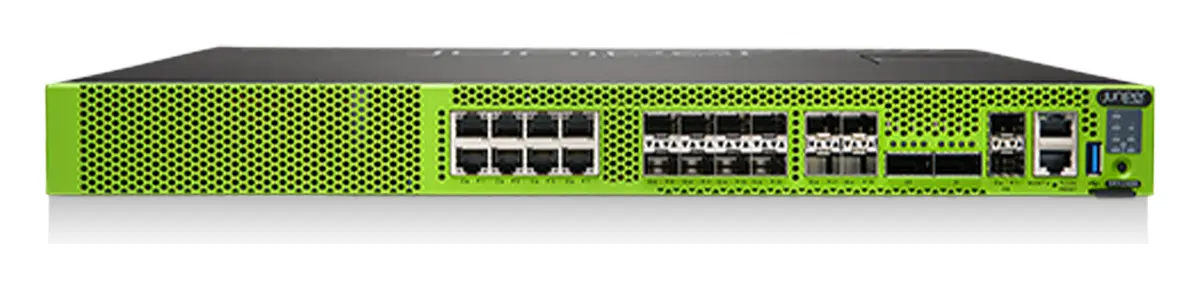
Juniper SRX2300 kullanım alanları ve özellikleri.
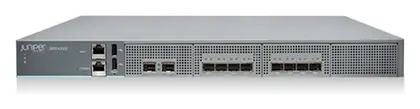
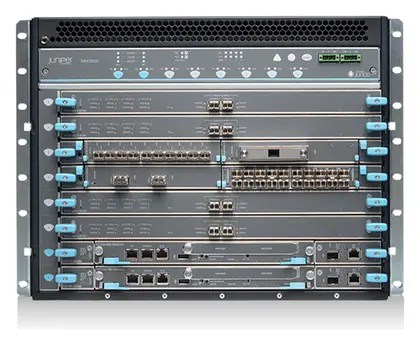
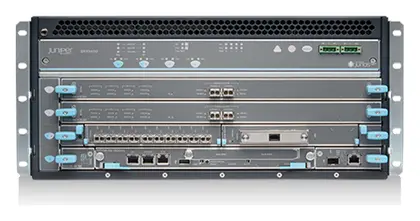
The Juniper Networks SRX2300 firewall is a high-performance, next-generation firewall (NGFW) designed to provide reliable network protection for your enterprise campus edge and data center edge.
The Juniper Networks SRX2300 firewall is a high performance, next-generation firewall (NGFW) designed to provide reliable network protection for your enterprise campus edge and data center edge. It also supports roaming, SD-WAN large branch, and SD-WAN secure hub use cases. Combining carrier-grade routing with state-of-the-art switching, this platform delivers robust security, effective threat detection, and comprehensive automation and mitigation capabilities.
The SRX2300 firewall delivers NGFW features that support the changing needs of cloud-enabled enterprise networks and data centers. Whether rolling out new services within an enterprise campus, connecting to the cloud seamlessly, complying with industry standards, or achieving operational efficiency, the SRX2300 empowers organizations to operationalize zero trust principles at scale while realizing their business objectives. The SRX2300 protects critical corporate assets with intrusion prevention system (IPS), follow-the-user and follow-the-application access policies, and HPE’s AI-Predictive Threat Prevention. Furthermore, the SRX2300 works with Juniper cloud security solutions to secure hybrid cloud environments with networkwide visibility and control, providing consistently secure on-premises and cloud environments.
As network architectures become more distributed and decentralized, Juniper Networks SRX Series firewalls ensure seamless integration with other Hewlett Packard Enterprise and third-party networking platforms. At the same time, the NGFWs facilitate architectural transformation, taking organizations from on-premises to hybrid cloud environments seamlessly and cost-effectively. SRX Series firewalls are the first to implement industry-standard Ethernet VPN (EVPN) Type 5 and Virtual Extensible LAN (VXLAN) protocols within data center environments, enabling the SRX2300 to act as a secure, fabric-aware leaf in the data center spine-leaf architecture.
The SRX2300 participates in the industry-first Connected Security Distributed Services Architecture, enabling organizations to scale horizontally and elastically and simplify the operational management of large-scale firewall networks. With this architecture, several SRX2300 platforms can work together as a single large logical firewall to provide higher performance and scale security.
The SRX2300 is powered by HPE’s industry-leading Junos operating system that underpins and helps secure the world’s largest mission-critical enterprise and service provider networks. It is managed by Juniper Security Director Cloud, Juniper’s unified management experience that connects the organization’s current deployments with future architectural rollouts. Security Director Cloud uses a single policy framework, enabling consistent security policies across any environment and expanding zero trust to all parts of the network—from the edge into the data center. This provides unbroken visibility, policy configuration, administration, and collective threat intelligence all in one place.
Dokümanlar
Veri sayfası ve kullanım kılavuzları.
Sık sorulanlar
SRX2300 hakkında kısa yanıtlar.
SRX2300 fiyatı ne kadar?
SRX2300 için fiyat; adet, proje kapsamı ve güncel kura göre değiştiğinden teklif usulüyle verilir. Ürünü teklif listenize ekleyerek veya telefon/WhatsApp hattımızdan ulaşarak aynı iş günü içinde fiyat ve stok bilgisi alabilirsiniz.
Hızlı teklif
Formu doldurun, SRX2300 için fiyat ve teslim süresini iletelim.
Benzer ürünler
Tümü Firewall & Ağ Güvenliği