Juniper
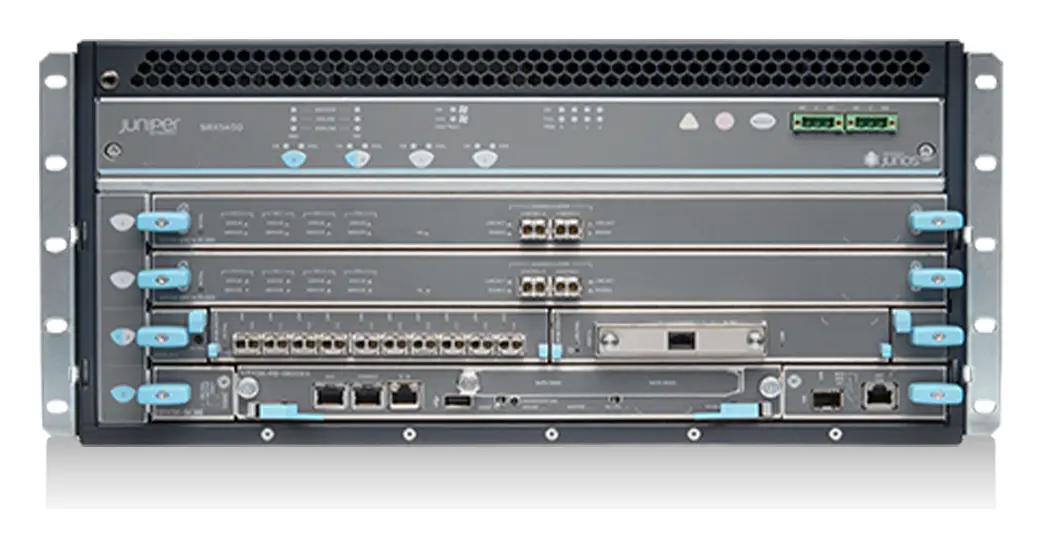
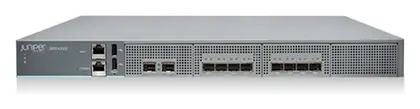
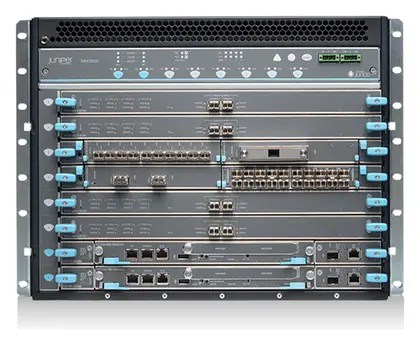
Juniper SRX5400 Firewall
Model
SRX5400Juniper SRX5400 firewall: Large enterprise data centers, Cloud and hosting provider data centers, Mobile operator environments, Managed service providers, Core service provider infrastructures.
Fiyat ve stok bilgisi alınAynı gün dönüş
Adet ve proje bilginize göre güncel fiyat, stok ve teslim süresini iletelim.
Distribütör garantili
81 ile sevkiyat
Teknik destek
- Large enterprise data centers
- Cloud and hosting provider data centers
- Mobile operator environments
- Managed service providers
- Core service provider infrastructures
Teknik özellikler
Üretici veri sayfasından derlenmiştir; proje öncesi güncel datasheet ile teyit edilmesi önerilir.
Teknik Özellikler 46 satır
| Junos OS version tested | Junos OS 21.2 |
|---|---|
| Firewall Performance, IMIX | 960 Gbps |
| Maximum performance per chassis | 960 Gbps |
| Next-Generation Datacenter Firewall Performance | 136 Gbps |
| Secure Web Access Firewall Performance | 75 Gbps |
| Latency (stateful firewall) | ~11µsec |
| IPSec VPN AES-256-GCM (IMIX) | 188 Gbps |
| Maximum IPS performance | 172 Gbps |
| Maximum concurrent sessions | 91 Million |
| New sessions/second (sustained, tcp, 3way, firewall NAT) | 1.7/1 Million |
| Maximum users supported | Unrestricted |
| Brute force attack mitigation | Yes |
| SYN cookie protection | Yes |
| Zone-based IP spoofing | Yes |
| Malformed packet protection | Yes |
| Attack detection mechanisms | Stateful signatures, protocol anomaly detection (zero-day coverage), application identification |
| Attack response mechanisms | Drop connection, close connection, session packet log, session summary, email |
| Attack notification mechanisms | Structured system logging |
| Worm protection | Yes |
| Simplified installation through recommended policies | Yes |
| Trojan protection | Yes |
| Spyware/adware/keylogger protection | Yes |
| Advanced malware protection | Yes |
| Reconnaissance protection | Yes |
| Request and response side attack protection | Yes |
| Custom attack signatures creation | Yes |
| Contexts accessible for customization | 600+ |
| Attack editing (port range, other) | Yes |
| Stream signatures | Yes |
| Protocol thresholds | Yes |
| Frequency of updates | Daily and emergency |
| Redirect web filtering | Yes |
| Antispam | Yes |
| Interface source NAT— interface DIP | Yes |
| Symmetric NAT | Yes |
| Allocate multiple ranges in NAT pool | Yes |
| Proxy Address Resolution Protocol (ARP) for physical port | Yes |
| Source NAT with loopback grouping—DIP with loopback grouping | Yes |
| Built-in (internal) database | Yes |
| RADIUS accounting | Yes |
| Web-based authentication | Yes |
| PKI certificate requests (PKCS 7, PKCS 10, and CMPv2) | Yes |
| Automated certificate enrollment (SCEP) | Yes |
| Certificate authorities supported | Yes |
| Self-signed certificates | Yes |
| Redundant fabric links | Yes |
Firewall 3 satır
| Network attack detection | Yes |
|---|---|
| DoS and distributed denial of service (DDoS) protection | Yes |
| TCP reassembly for fragmented packet protection | Yes |
IPSec VPN 18 satır
| Site-to-site tunnels | 15,000 |
|---|---|
| Tunnel interfaces | 15,000 |
| Number of remote access / SSL VPN (concurrent) users | 25,000 |
| Tunnels | Site-to-Site, Hub and Spoke, Dynamic Endpoint, AutoVPN, ADVPN, Group VPN (IPv4 / IPv6 / Dual Stack) |
| Configuration payload | Yes |
| IKE Authentication Algorithms | MD5, SHA1, SHA-256, SHA-384, SHA-512 |
| IKE Encryption Algorithms | Prime, DES-CBC, 3DES-CBC, AEC-CBC, AES-GCM, SuiteB |
| Authentication | Pre-shared key and public key infrastructure (PKI X.509) |
| IPSec (Internet Protocol Security) | Authentication Header (AH) / Encapsulating Security Payload (ESP) protocol |
| IPSec Authentication Algorithms | hmac-md5, hmac-sha-196, hmac-sha-256, hmac-sha-384, hmac-sha-512 |
| IPSec Encryption Algorithms | Prime, DES-CBC, 3DES-CBC, AEC-CBC, AES-GCM, SuiteB |
| Monitoring | Standard-based Dead peer detection (DPD), VPN monitoring |
| Prevent replay attack | Yes |
| VPNs (GRE, IP-in-IP, MPLS) | Yes |
| Redundant VPN gateways | Yes |
| Signature-based and customizable (via templates) | Yes |
| Active/active traffic monitoring | Yes |
| Stateful protocol signatures | Yes |
Content security 3 satır
| Antivirus | Yes |
|---|---|
| Content filtering | Yes |
| Enhanced web filtering | Yes |
AppSecure 4 satır
| AppTrack (application visibility and tracking) | Yes |
|---|---|
| AppFirewall (policy enforcement by application name) | Yes |
| AppQoS (network traffic prioritization by application name) | Yes |
| User-based application policy enforcement | Yes |
GPRS security 11 satır
| GPRS stateful firewall | Yes |
|---|---|
| Destination NAT with Port Address Translation (PAT) | Yes |
| Destination NAT within same subnet as ingress interface IP | Yes |
| Destination addresses to one single address (M:1) | Yes |
| Destination addresses to another range of addresses (M:M) | Yes |
| Source NAT with PAT—port translated | Yes |
| Source NAT without PAT—fix port | Yes |
| Source NAT—IP address persistency | Yes |
| Source pool grouping | Yes |
| Source pool utilization alarm | Yes |
| Source IP outside of the interface subnet | Yes |
Virtualization 3 satır
| Maximum custom routing instances with data plane separation | 2000 |
|---|---|
| Maximum security zones | 2000 |
| Maks. VLAN Sayısı | 4096 |
Routing 14 satır
| BGP instances | 1000 |
|---|---|
| BGP peers | 2000 |
| BGP routes | 1 million |
| OSPF instances | 400 |
| OSPF routes | 1 million |
| RIP v1/v2 instances | 50 |
| RIP v2 table size | 30,000 |
| Dynamic routing | Yes |
| Static routes | Yes |
| Source-based routing | Yes |
| Policy-based routing | Yes |
| Equal cost multipath (ECMP) | Yes |
| Reverse path forwarding (RPF) | Yes |
| Multicast | Yes |
IPv6 7 satır
| Firewall/stateless filters | Yes |
|---|---|
| Dual-stack IPv4/IPv6 firewall | Yes |
| RIPng | Yes |
| BFD, BGP | Yes |
| ICMPv6 | Yes |
| OSPFv3 | Yes |
| Class of service (CoS) | Yes |
Mode of operation 2 satır
| Layer 2 (transparent) mode | Yes |
|---|---|
| Layer 3 (route and/or NAT) mode | Yes |
IP address assignment 15 satır
| Static | Yes |
|---|---|
| Dynamic Host Configuration Protocol (DHCP) | Yes |
| Internal DHCP server | Yes |
| DHCP relay | Yes |
| Maximum bandwidth | Yes |
| RFC2474 IP DiffServ in IPv4 | Yes |
| Firewall filters for CoS | Yes |
| Classification | Yes |
| Scheduling | Yes |
| Shaping | Yes |
| Intelligent Drop Mechanisms (WRED) | Yes |
| Three-level scheduling | Yes |
| Weighted round robin for each level of scheduling | Yes |
| Priority of routing protocols | Yes |
| Traffic management/ policing in hardware | Yes |
High Availability (HA) 8 satır
| Active/passive, active/active | Yes |
|---|---|
| Unified in-service software upgrade (unified ISSU) | Yes |
| Configuration synchronization | Yes |
| Session synchronization for firewall and IPSec VPN | Yes |
| Session failover for routing change | Yes |
| Device failure detection | Yes |
| Link and upstream failure detection | Yes |
| Dual control links | Yes |
Management 3 satır
| WebUI (HTTP and HTTPS) | Yes |
|---|---|
| Command line interface (console, telnet, SSH) | Yes |
| Juniper Security Director Cloud | Yes |
Administration 6 satır
| Local administrator database support | Yes |
|---|---|
| External administrator database support | Yes |
| Restricted administrative networks | Yes |
| Root admin, admin, and read-only user levels | Yes |
| Software upgrades | Yes |
| Configuration rollback | Yes |
Logging/monitoring 3 satır
| Structured syslog | Yes |
|---|---|
| SNMP (v2 and v3) | Yes |
| Traceroute | Yes |
Certificatiions 6 satır
| Safety certifications | Yes |
|---|---|
| Electromagnetic Compatibility (EMC) certifications | Yes |
| RoHS2 Compliant (European Directive 2011/65/EU) | Yes |
| NIST FIPS-140-2 Level | Yes |
| Common Criteria NDPP+TFFW EP + VPN EP | Yes |
| USGv6 | Yes |
Boyutlar ve Güç 6 satır
| Dimensions (W x H x D) | 17.45 x 8.7 x 24.5 in (44.3 x 22.1 x 62.2 cm) |
|---|---|
| Ağırlık | Fully configured 128 lb (58.1 kg) |
| Power supply (AC) | 100 to 240 VAC |
| Power supply (DC) | -40 to −60 VDC |
| Maximum power | 4,100 watts (AC high capacity) |
| Typical power | 1540 watts |
Ortam Koşulları 3 satır
| Operating temperature – long term | 41°F to 104°F (5°C to 40°C) |
|---|---|
| Humidity – long term | 5% to 85% noncondensing |
| Humidity – short term | 5% to 93% noncondensing but not to exceed 0.026 kg water/kg of dry air |
Genel bakış
Juniper SRX5400 kullanım alanları ve özellikleri.
This data sheet provides overview of the Juniper Networks SRX5400, SRX5600, and SRX5800, next-generation firewalls, that deliver industry-leading threat protection, high performance, six nines reliability, scalability, and services integration.
The SRX Series next-generation firewalls are built for large enterprise data centers, service provider infrastructure, and public sector networks. With a modular architecture and high performance line cards, the SRX Series firewalls are open, scalable security platforms with flexible connectivity options and service integration. The award-winning SRX Series is powered by Junos OS, the same industry-leading operating system that keeps the world’s largest data center networks available, manageable, and secure.
The SRX5400, SRX5600, and SRX5800 are managed by Juniper Security Director Cloud, a unified management experience that connects current deployments with their future architectural rollouts. Security Director Cloud uses a single policy framework enabling consistent security policies across any environment and expands zero trust to all parts of the network from the edge into the data center. This provides unbroken visibility, policy configuration, administration, and collective threat intelligence all in one place.
The SRX5000 line provides unrivaled scalability and performance. Each firewall scales with the addition of Services Processing Cards (SPCs) and I/O cards (IOCs), enabling a fully equipped SRX5800 to support up to 3.36 Tbps firewall throughput. The SPCs are designed to support a range of services, enabling future support of new capabilities without the need for service-specific hardware.
The SRX5400, SRX5600, and SRX5800 firewalls are an integral part of the Juniper(R) Connected Security framework, which extends security to every point of connection on the network to safeguard applications, user, and infrastructure from advanced threats. Delivering the highest level of protection against exploits, malware, and command and control (C&C) communications, these platforms feature a carrier-grade next-generation firewall and advanced security services such as application security, intrusion prevention system (IPS), and integrated threat intelligence services.
Using SPCs on all services ensures that there are no idle resources based on specific services being used maximizing hardware utilization.
- Large enterprise data centers
- Cloud and hosting provider data centers
- Mobile operator environments
- Managed service providers
- Core service provider infrastructures
Dokümanlar
Veri sayfası ve kullanım kılavuzları.
Sık sorulanlar
SRX5400 hakkında kısa yanıtlar.
SRX5400 fiyatı ne kadar?
SRX5400 için fiyat; adet, proje kapsamı ve güncel kura göre değiştiğinden teklif usulüyle verilir. Ürünü teklif listenize ekleyerek veya telefon/WhatsApp hattımızdan ulaşarak aynı iş günü içinde fiyat ve stok bilgisi alabilirsiniz.
Hızlı teklif
Formu doldurun, SRX5400 için fiyat ve teslim süresini iletelim.
Benzer ürünler
Tümü Firewall & Ağ Güvenliği